Archive for Cybersecurity - page 53

Advancing Opportunities for Women in Cybersecurity through Global Partnerships

Fortinet works with numerous partners to offer programs that focus on providing more access to training, education, and career opportunities for women interested in cybersecurity. Learn more. Source link Author: Fortinet Article used for cyber security disclosure.

Continue reading →

CISA Warns of Sitecore RCE Flaws; Active Exploits Hit Next.js and DrayTek Devices

CISA Warns of Sitecore RCE Flaws; Active Exploits Hit Next.js and DrayTek Devices

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added two six-year-old security flaws impacting Sitecore CMS and Experience Platform (XP) to its Known Exploited Vulnerabilities (KEV) catalog, based on evidence of active exploitation. The vulnerabilities are listed below – CVE-2019-9874 (CVSS score: 9.8) –…

Continue reading →

New Security Flaws Found in VMware Tools and CrushFTP — High Risk, No Workaround

New Security Flaws Found in VMware Tools and CrushFTP — High Risk, No Workaround

Broadcom has issued security patches to address a high-severity security flaw in VMware Tools for Windows that could lead to an authentication bypass. Tracked as CVE-2025-22230, the vulnerability is rated 7.8 on the ten-point Common Vulnerability Scoring System (CVSS). “VMware Tools for Windows contains an…

Continue reading →

Life at Fortinet: Breaking Cybersecurity Misconceptions

Cybersecurity is a highly collaborative, strategic, and business-driven industry that has a direct impact on people, businesses, and critical infrastructures. Source link Author: Fortinet Article used for cyber security disclosure.
Continue reading →

CISA Releases Four Industrial Control Systems Advisories

CISA released four Industrial Control Systems (ICS) advisories on March 25, 2025. These advisories provide timely information about current security issues, vulnerabilities, and exploits surrounding ICS. ICSA-25-084-01 ABB RMC-100 ICSA-25-084-02 Rockwell Automation Verve Asset Manager ICSA-25-084-03 Rockwell Automation 440G TLS-Z ICSA-25-084-04 Inaba Denki Sangyo CHOCO…

Continue reading →

Zero-Day Alert: Google Releases Chrome Patch for Exploit Used in Russian Espionage Attacks

Zero-Day Alert: Google Releases Chrome Patch for Exploit Used in Russian Espionage Attacks

Google has released out-of-band fixes to address a high-severity security flaw in its Chrome browser for Windows that has been exploited in the wild as part of attacks targeting organizations in Russia.  The vulnerability, tracked as CVE-2025-2783, has been described as a case of “incorrect…

Continue reading →

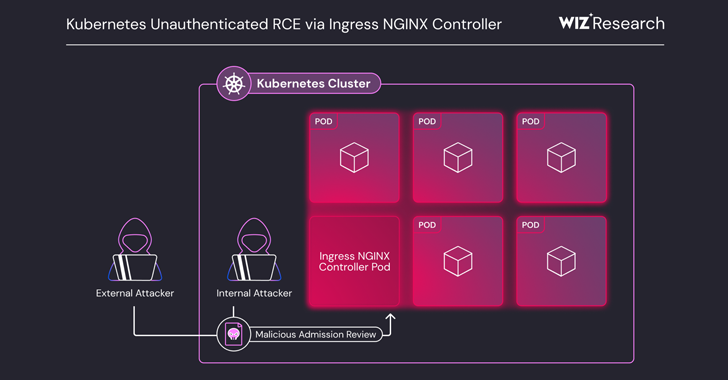
Critical Ingress NGINX Controller Vulnerability Allows RCE Without Authentication

Critical Ingress NGINX Controller Vulnerability Allows RCE Without Authentication

A set of five critical security shortcomings have been disclosed in the Ingress NGINX Controller for Kubernetes that could result in unauthenticated remote code execution, putting over 6,500 clusters at immediate risk by exposing the component to the public internet. The vulnerabilities (CVE-2025-24513, CVE-2025-24514, CVE-2025-1097,…

Continue reading →

Customs Agency Enhances Security and Cuts Costs with Fortinet Unified SASE

With Fortinet Unified SASE, a customs agency has modernized its network, enhancing security, efficiency, and workforce productivity while significantly reducing costs. Source link Author: Fortinet Article used for cyber security disclosure.
Continue reading →

Page 53 of 198 ← First ... ← 51 52 53 54 55 → ... Last →